Shift Left. Secure Your Code from Commit to
Cloud with AI AutoFix.
Identify vulnerabilities, hardcoded secrets, misconfigured Infrastructure as Code (IaC), and vulnerable open-source dependencies directly in your IDE or CI/CD pipelines—before they ever reach production
Shift Left. Secure Your Code from Commit to Cloud with AI AutoFix.
Identify vulnerabilities, hardcoded secrets, misconfigured Infrastructure as Code (IaC), and vulnerable open-source dependencies directly in your IDE or CI/CD pipelines—before they ever reach production
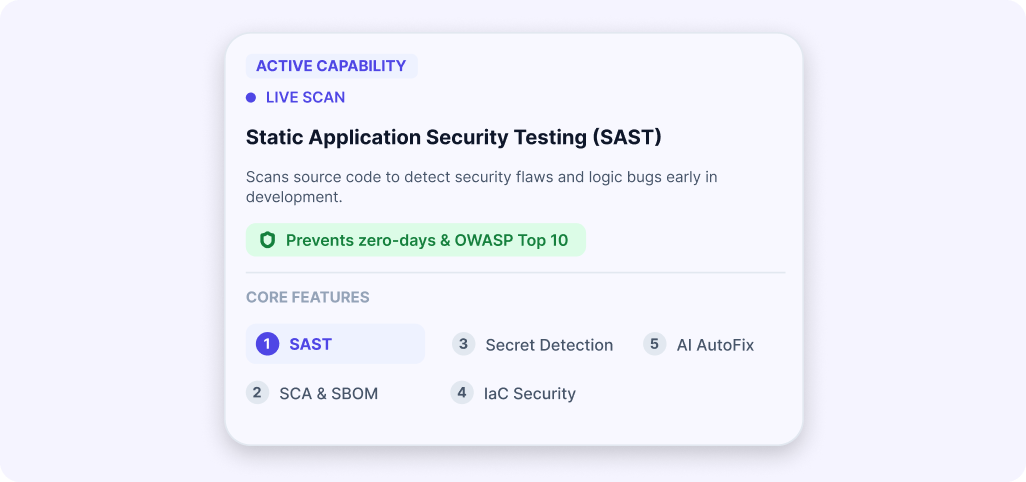
Scans custom source code across multi-language projects to detect security flaws, code quality issues, and logic bugs early in development.
Value: Prevents zero-day vulnerabilities & OWASP Top 10 risks
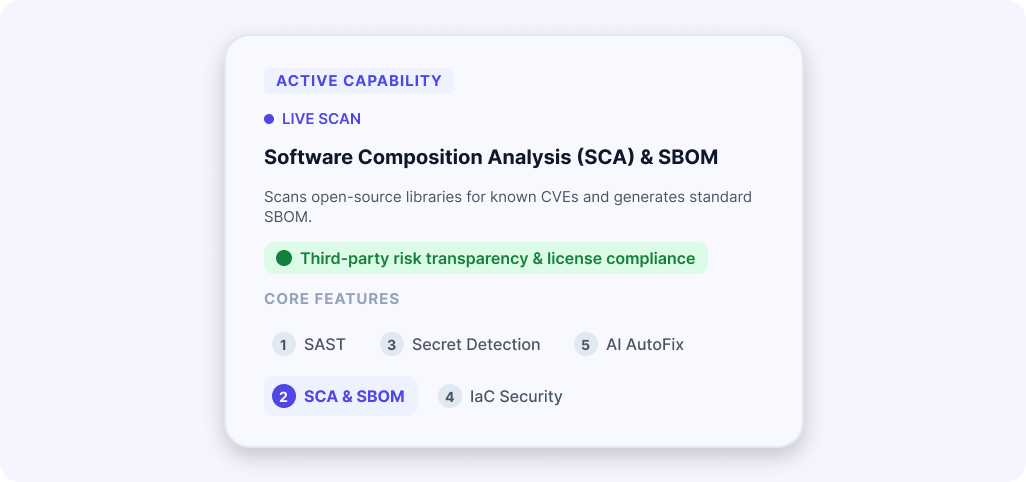
Software Composition Analysis (SCA) & SBOM SBOM
Scans open-source libraries, third-party packages, and outdated software for known CVEs. Automatically generates standard Software Bill of Materials (SBOM).
Value: Maintains total transparency over third-party component risks and open-source license compliance.
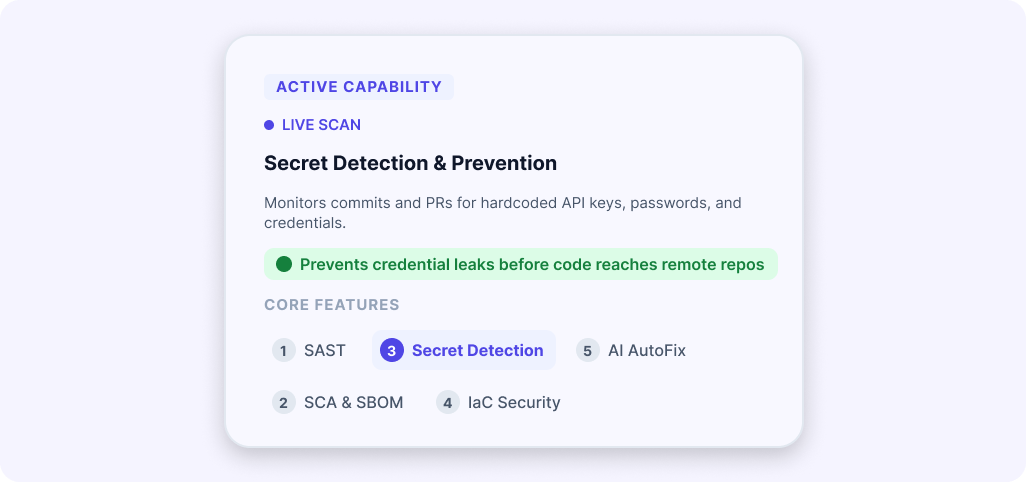
Secret Detection & Prevention
Continuously monitors code commits, pull requests, and history for hardcoded API keys, passwords, database credentials, and SSH keys.
Value: Prevents credential leaks before code gets pushed to remote Git platforms (GitHub, GitLab, Bitbucket).
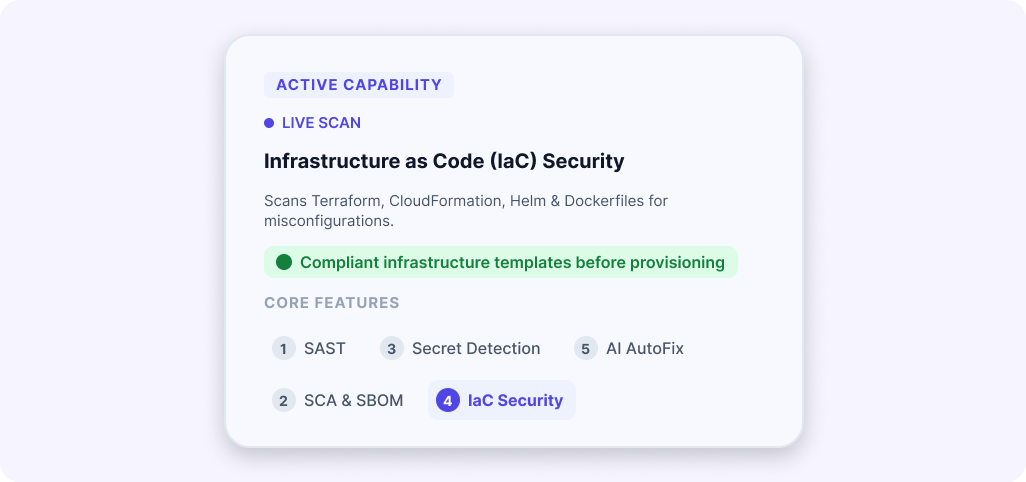
Infrastructure as Code (IaC) Security IaC
Scans Terraform, CloudFormation, Helm charts, and Dockerfiles to find infrastructure misconfigurations prior to deployment.
Value: Ensures your infrastructure templates comply with security standards before provisioning cloud resources.
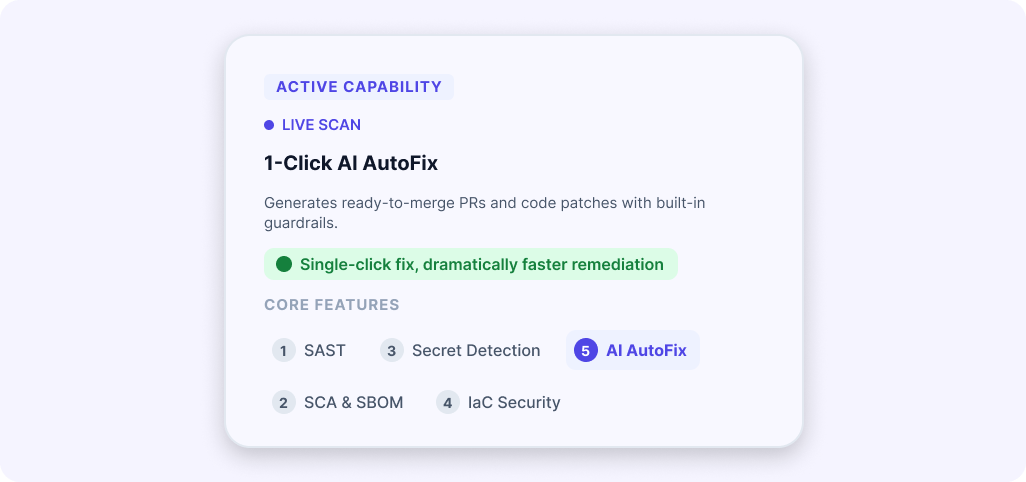
1-Click AI AutoFix AutoFix
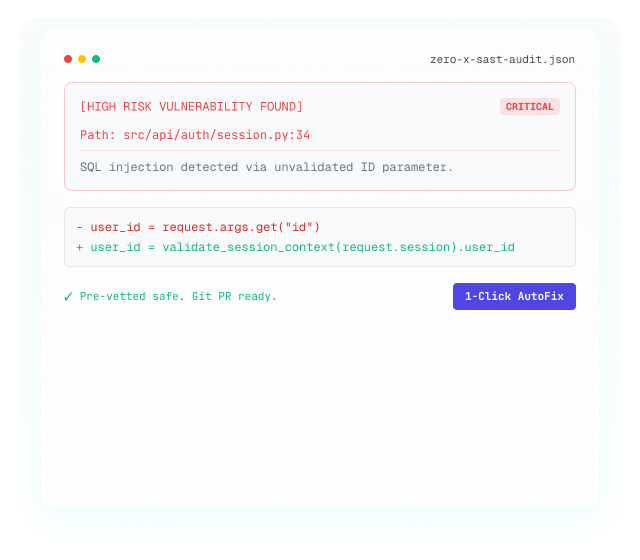
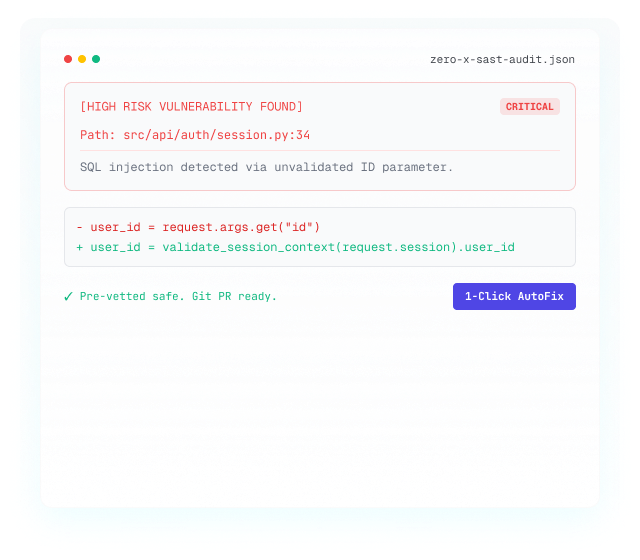
Instead of surfacing endless alerts, ZERO-X generates ready-to-merge Pull Requests (PRs) and automated code patches with built-in guardrails.
Value: Transforms hours of developer investigation into a single-click fix, dramatically accelerating remediation time.
key Capabilities
Core Features
How It Works
From Connection to Control in Under 10 Minutes
2026-09-19 T14:32:07 • STEP 01
Fast Developer Onboarding
05 MIN
Connect your repositories (GitHub, GitLab, Bitbucket) or IDEs in under 5 minutes through secure, lightweight integrations.
2026-09-19 T14:32:07 • STEP 02
Automated Pipeline Scanning
Trigger automatic static scans, dependency analysis, and secret detection on every Git commit or Pull Request.
2026-09-19 T14:32:07 • STEP 03
Unified Context & Prioritization
Correlate code vulnerabilities with runtime cloud environments to prioritize critical attack paths over false positives.
2026-09-19 T14:32:07 • AUTO-FIX DEPLOYED
AI-Driven 1-Click Remediation
Generate Git branch PRs and code updates automatically—allowing developers to resolve risks directly within their workflow.
Why Choose Us?
The Zero-X Cloud Advantage
Legacy Security Tools
Disconnected security tools create friction between Dev & Sec.
Security teams file tickets; developers fix issues manually.
Overwhelmed by false positives and alert noise across multiple security monitoring systems.
Manual software inventory tracking.
ZERO-X Code & Application Security
Unified Code-to-Cloud Platform bridges developer
tools with cloud runtime.
AI AutoFix automatically generates Pull Requests
to fix flaws instantly.
Risk-Based Prioritization surfaces only actionable, high-impact threats.
Automated SBOM Generation for real-time visibility into software supply chains.
Why Choose Us?
Why ZERO-X Code Security?
Legacy Security Tools
Disconnected Security Tools Create Friction Between Dev & Sec.
Security Teams File Tickets; Developers Fix Issues Manually.
Overwhelmed By False Positives And Alert Noise.
Manual Software Inventory Tracking.
VS
ZERO-X Code & Application Security
Unified Code-To-Cloud Platform Bridges Developer Tools With Cloud Runtime.
AI AutoFix Automatically Generates Pull Requests To Fix Flaws Instantly.
Risk-Based Prioritization Surfaces Only Actionable, High-Impact Threats.
Automated SBOM Generation For Real-Time Visibility Into Software Supply Chains.
Swipe to compare→
Developer & DevOps Stack Integrations
SCM / VCS
CI/CD Pipelines
IaC & Containers
Cloud Environments
Developer & DevOps Stack Integrations
SCM / VCS
CI/CD Pipelines
IaC & Containers
Cloud Environments
Intergrations
Works With Your Existing Stack
Effortlessly connect your projects from different cloud and code platforms.
ZERO-X connects natively with popular source control management tools (GitHub, GitLab, Bitbucket) and CI/CD pipelines. You can also integrate it into developer IDEs for instant, real-time feedback prior to pushing code.
When ZERO-X identifies a vulnerability (such as a vulnerable package version, an IaC misconfiguration, or a SAST flaw), our AI engine generates a precise fix or code patch and opens a ready-to-merge Pull Request (PR) in your repository with built-in guardrails.
A Software Bill of Materials (SBOM) is a complete nested inventory of every third-party component, library, and dependency used in your application software. ZERO-X automatically generates and updates your SBOM to assist with supply chain security and compliance audits.
No. ZERO-X uses optimized, lightweight scanners engineered to execute rapid, incremental checks on changed files, ensuring your deployment speed remains fast and uninterrupted.
Start AutoFixing Vulnerabilities Today
AutIntegrate the Zero-X engine in under 10 minutes. Cut your remediation time by 70% and let developers focus on building.
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.