Fix Vulnerabilities in Seconds with 1-Click AutoFix

Turn complex SAST, SCA, IaC, and Container security findings into merge-ready Pull Requests.
Zero-X automatically patches code vulnerabilities without breaking your builds or interrupting developer workflows

Read-Only Access

We propose PRs—we never alter your code directly.

Fast Remediation

Generates tested patches in under 5 seconds

Zero Code Storage

Your source code is processed transiently and never saved.

Fix Vulnerabilities in Seconds with 1-Click AutoFix

Turn complex SAST, SCA, IaC, and Container security findings into merge-ready Pull Requests.
Zero-X automatically patches code vulnerabilities without breaking your builds or interrupting developer workflows

key Capabilities

Automated Remediation Built for Scale

SAST Code Remediation

Code-Aware Fixes
in Under 5 Seconds

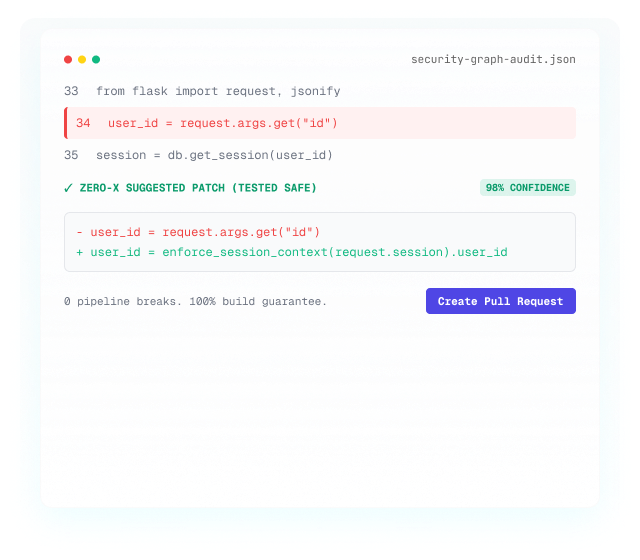
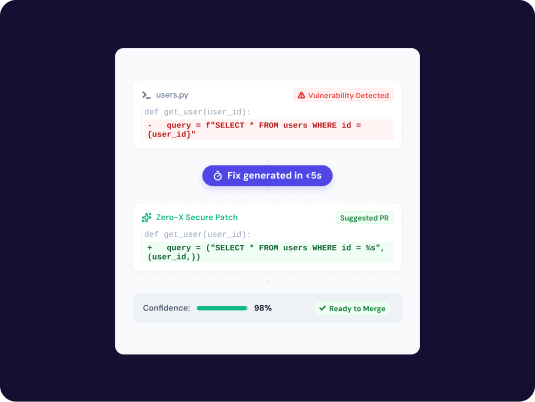
Eliminate code-level vulnerabilities as soon as they’re committed. Zero-X generates precise patches directly in your workflow, complete with a Confidence Score so you know exactly how reliable every fix is before merging.

Smart Dependency Upgrades (SCA)

Patch Package CVEs
Without Breaking Your Build

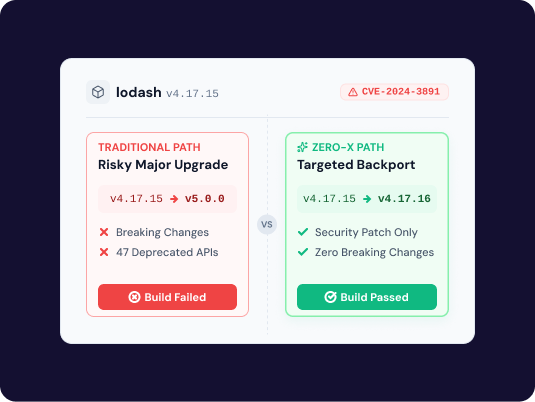
Traditional security tools force risky major updates that break production. Zero-X calculates the smallest safe version bump to resolve vulnerabilities, or backports security fixes directly onto the exact library version you’re already using.

Container & Dockerfile Patching

Multi-Option
Container Hardening

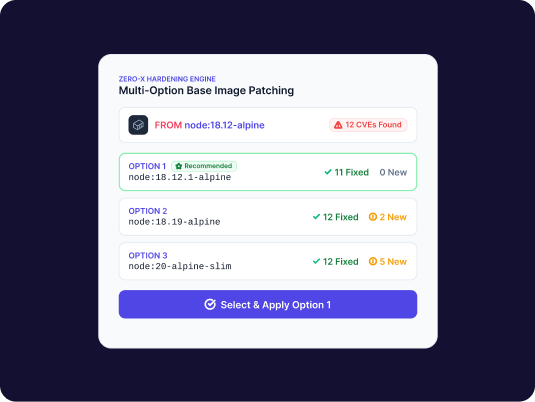
Zero-X scans your Dockerfiles and generates 3 to 5 tailored base image patch options. Easily compare fixed vulnerabilities against new risks before selecting the best base image for your deployment stack.

Interactive AI Refinement

Refine Code Patches
Without Leaving the Platform

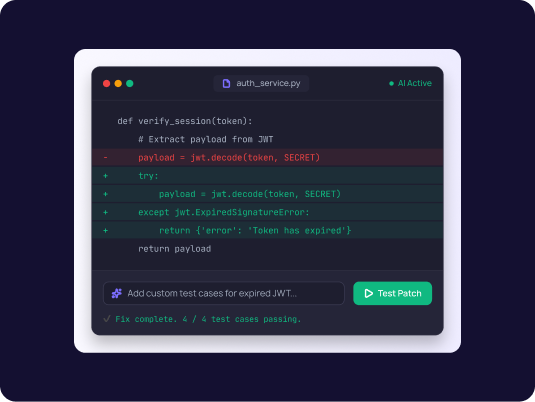
Need a different error-handling pattern or custom test cases? Instruct Zero-X AI directly in the dashboard to adjust the proposed code. Update and test patches in real time without jumping between IDEs or external AI tools.

key Capabilities

Automated Remediation Built for Scale

Code-Aware Fixes in Under 5 Seconds

Eliminate code-level vulnerabilities as soon as they’re committed. Zero-X generates precise patches directly in your workflow, complete with a Confidence Score so you know exactly how reliable every fix is before merging.

Patch Package CVEs Without Breaking Your Build

Traditional security tools force risky major updates that break production. Zero-X calculates the smallest safe version bump to resolve vulnerabilities, or backports security fixes directly onto the exact library version you’re already using.

Multi-Option Container Hardening

Zero-X scans your Dockerfiles and generates 3 to 5 tailored base image patch options. Easily compare fixed vulnerabilities against new risks before selecting the best base image for your deployment stack.

Refine Code Patches Without Leaving the Platform

Need a different error-handling pattern or custom test cases? Instruct Zero-X AI directly in the dashboard to adjust the proposed code. Update and test patches in real time without jumping between IDEs or external AI tools.

How It Works

Detect

Zero-X continuously scans your repositories, pull requests, and container images for SAST, SCA, secrets, and configuration flaws.

Generate

The AutoFix engine crafts a precise patch in seconds, complete with inline context and a safety confidence rating.

Merge

Review the proposed diff in your IDE or GitHub/GitLab, refine it with AI if needed, and merge with 1 click.

How It Works

Detect

Zero-X continuously scans your repositories, pull requests, and container images for SAST, SCA, secrets, and configuration flaws.

Generate

The AutoFix engine crafts a precise patch in seconds, complete with inline context and a safety confidence rating.

Merge

Review the proposed diff in your IDE or GitHub/GitLab, refine it with AI if needed, and merge with 1 click.

Why Developers Choose Zero-X Cloud

Zero Friction

AutoFix opens ready-to-merge pull requests instantly when a vulnerability is flagged.

Add your main image URL in the JavaScript section below.

Non-Breaking Guarantee

Smart version bumps ensure your CI/CD pipelines stay green.

Custom Workflows

Set custom branch names, commit conventions, and merge criteria that fit your engineering standards.

Inline Feedback

Get line-level security recommendations directly inside pull request comments or your IDE editor.

key Capabilities

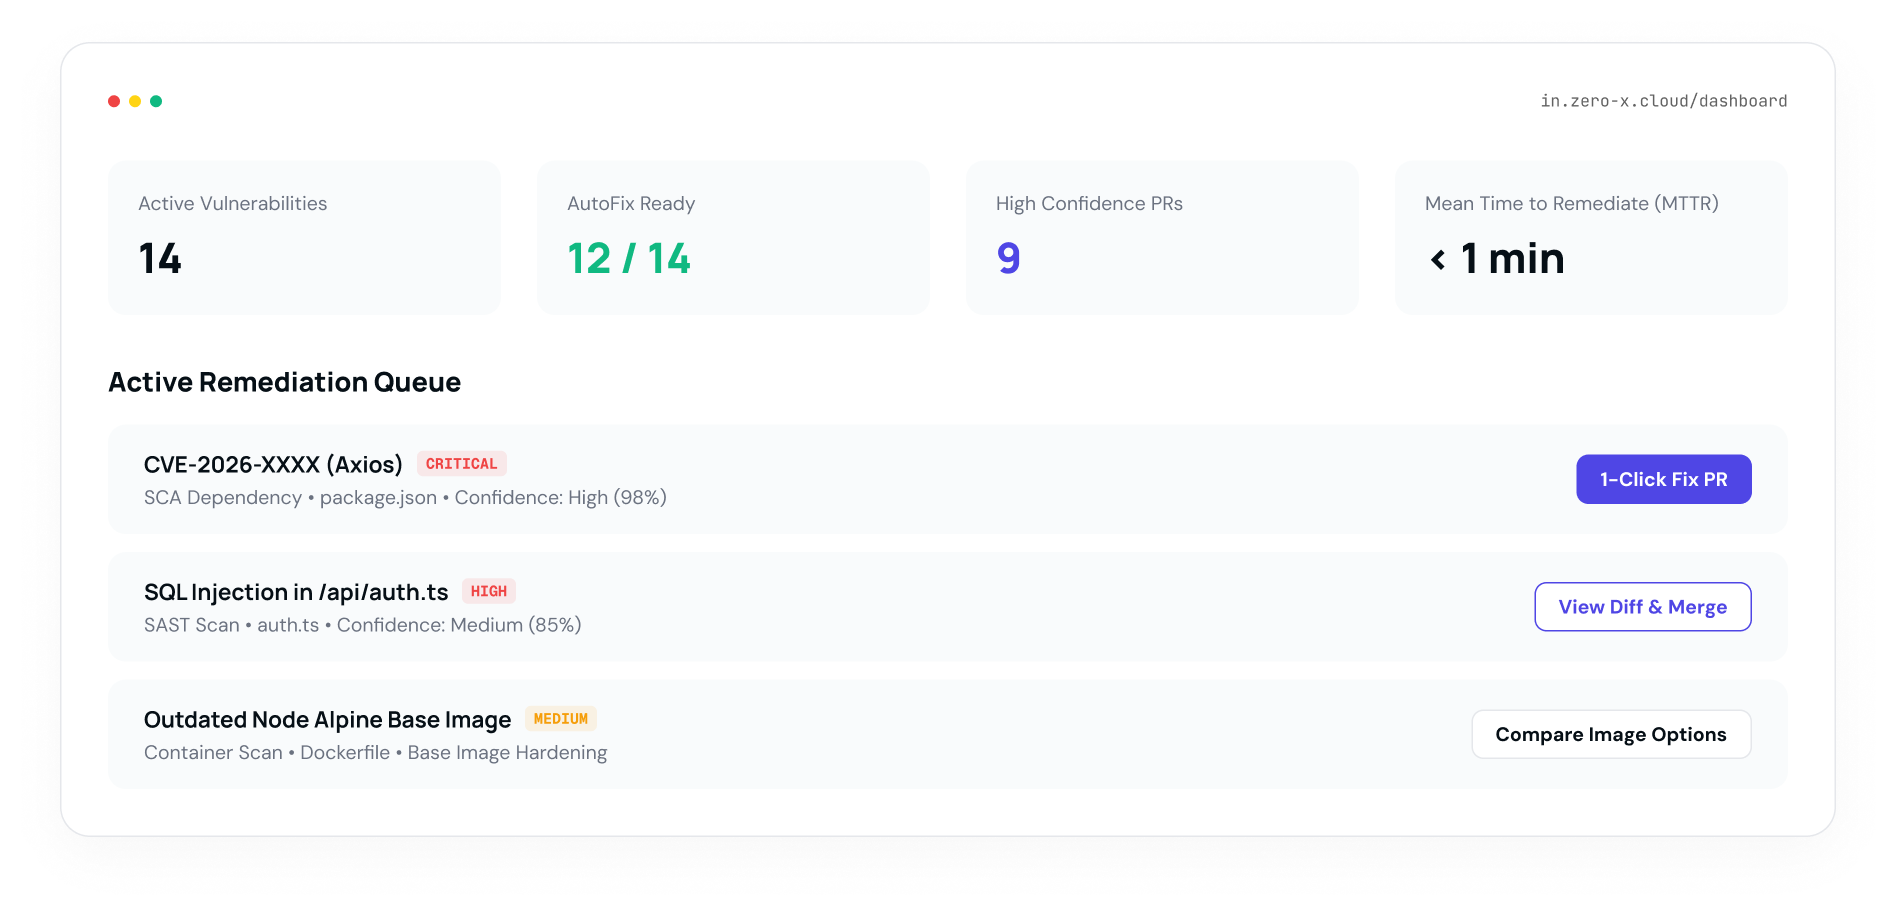
Dashboard Integration Overview

Intergrations

Works With Your Existing Stack

Effortlessly connect your projects from different cloud and code platforms.

FREQUENTLY ASKED QUESTIONS

Common Questions

No. Zero-X operates on strict read-only permissions to scan code. All generated security patches are delivered via standard Pull Requests / Merge Requests for your team to review and approve.

Zero-X processes your source code in temporary, volatile memory strictly for vulnerability analysis and patch creation. Your code is destroyed immediately after analysis and is never stored on our servers.

Yes. You can launch a sandboxed demo repository in 1 click from your dashboard to experience the full scanning and AutoFix workflow using sample code.

Start AutoFixing Vulnerabilities Today

AutIntegrate the Zero-X engine in under 10 minutes. Cut your remediation time by 70%
and let developers focus on building.

Start AutoFixing Vulnerabilities Today

AutIntegrate the Zero-X engine in under 10 minutes. Cut your remediation time by 70% and let developers focus on building.

Scroll to Top