
"As multi-cloud ecosystems grow, managing access rights across thousands of human and non-human identities (service accounts, bots, microservices) becomes impossible to handle manually.
Gain Complete Control Over Cloud Identities & Entitlements with ZERO-X CIEM
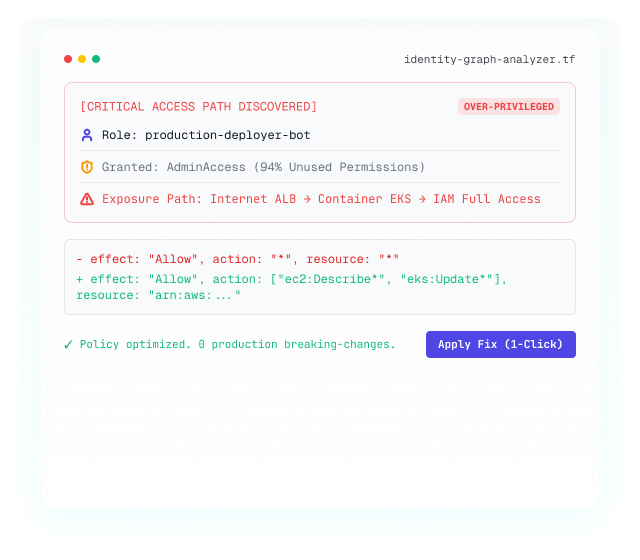
Detect over-privileged accounts, eliminate unused permissions and enforce True Zero Trust across multi-cloud environments all from a single, intelligent dashboard.
Gain Complete Control Over Cloud Identities & Entitlements with ZERO-X CIEM
Detect over-privileged accounts, eliminate unused permissions and enforce True Zero Trust across multi-cloud environments all from a single, intelligent dashboard.
The Challenge: The Cloud Permission Gap
Why Cloud Identity is the New
Attack Surface
Over 80%
Of cloud permissions go completely unused, creating invisible access paths for cyber attackers.
Excessive Permissions
Uncontrolled access rights increase your cloud exposure.
Machine Identities
Non-human identities now outnumber human users 10:1.
Permission Creep
Legacy IAM permissions accumulate over time without continuous oversight.
The ZERO-X Cloud Solution
Enforce Least Privilege Access Across
Every Cloud Infrastructure
ZERO-X CIEM continuously maps, analyzes, and rightsizes permissions across AWS, Azure, GCP and Kubernetes. We bridge the gap between granted access and actual usage so you can maintain a Zero-Trust posture effortlessly.
The Challenge: The Cloud Permission Gap
Why Cloud Identity is the New
Attack Surface
"As multi-cloud ecosystems grow, managing access rights across thousands of human and non-human identities (service accounts, bots, microservices) becomes impossible to handle manually.
Over 80%
Of cloud permissions go completely unused, creating invisible access paths for cyber attackers.
Excessive Permissions
Uncontrolled access rights increase your cloud exposure.
Machine Identities
Non-human identities now outnumber human users 10:1.
Permission Creep
Legacy IAM permissions accumulate over time without continuous oversight.
The ZERO-X Cloud Solution
Enforce Least Privilege Access Across Every Cloud Infrastructure
ZERO-X CIEM continuously maps, analyzes, and rightsizes permissions across AWS, Azure, GCP and Kubernetes. We bridge the gap between granted access and actual usage so you can maintain a Zero-Trust posture effortlessly.
Core Features & Capabilities
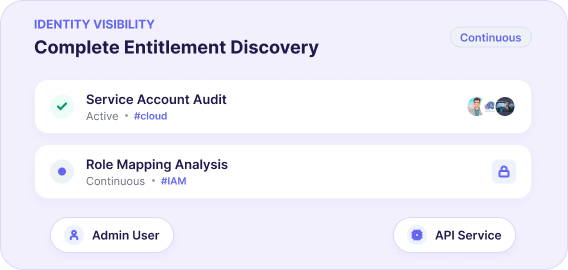
Complete Identity & Entitlement Discovery
Continuous visibility into every human user, service account, role, and non-human identity across your cloud environments
Benefit: Uncover hidden access pathways, nested group memberships and cross-account roles in seconds.
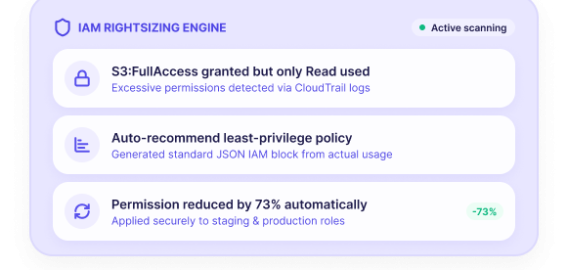
Automatic Permission Rightsizing
Contrast granted IAM permissions with real-world
activity logs.
Benefit: Identify unused or over-privileged roles and automatically generate tight, right-sized access policies.
Non-Human Identity Governance
Dedicated protection for service accounts, API keys and machine workloads.
Benefit: Prevent attackers from exploiting static credentials or over-privileged service roles across critical systems.
Just-In-Time & Temporary Access
Eliminate permanent administrative privileges across all user accounts.
Benefit: Grant time-bound, elevated access to developers and operators only when needed, automatically revoking access after execution.
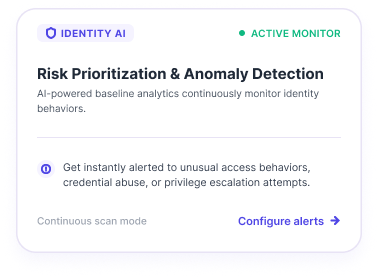
Risk & Anomaly Detection
AI-powered baseline analytics continuously monitor identity behaviors.
Benefit: Get instantly alerted to unusual access behaviors, credential abuse, or privilege escalation attempts.
Core Features & Capabilities
Complete Identity & Entitlement Discovery
Continuous visibility into every human user, service account, role, and non-human identity across your cloud environments
Benefit: Uncover hidden access pathways, nested group memberships and cross-account roles in seconds.
Automatic Permission Rightsizing
Contrast granted IAM permissions with real-worldactivity logs.
Benefit: Identify unused or over-privileged roles and automatically generate tight, right-sized access policies.
Non-Human Identity Governance
Dedicated protection for service accounts, API keys and machine workloads.
Benefit: Prevent attackers from exploiting static credentials or over-privileged service roles across critical systems.
Just-In-Time & Temporary Access
Eliminate permanent administrative privileges across all user accounts.
Benefit: Grant time-bound, elevated access to developers and operators only when needed, automatically revoking access after execution.
Risk & Anomaly Detection
AI-powered baseline analytics continuously monitor identity behaviors.
Benefit: Get instantly alerted to unusual access behaviors, credential abuse, or privilege escalation attempts.
How ZERO-X CIEM Works
Connect
Seamlessly link your multi-cloud accounts (AWS, Azure, GCP) via agentless API integrations in minutes.
Analyze
ZERO-X scans identity configurations, policy attachments and operational audit logs to build a permission usage baseline.
Rightsize
Receive actionable recommendations and 1-click remediation scripts to remove risky or unused privileges.
Govern
Continuously track access drift, enforce guardrail and generate compliance reports for audit readiness.
How ZERO-X CIEM Works
Connect
Seamlessly link your multi-cloud accounts (AWS, Azure, GCP) via agentless API integrations in minutes.
Analyze
ZERO-X scans identity configurations, policy attachments and operational audit logs to build a permission usage baseline.
Rightsize
Receive actionable recommendations and 1-click remediation scripts to remove risky or unused privileges.
Govern
Continuously track access drift, enforce guardrail and generate compliance reports for audit readiness.
Intergrations
Works With Your Existing Stack
Effortlessly connect your projects from different cloud and code platforms.
FREQUENTLY ASKED QUESTIONS
Common Questions
Identity and Access Management (IAM) allows you to set up users and grant permissions. CIEM provides the analytics layer that continuously monitors if those permissions are actually being used. It identifies permission creep, over-privileged accounts, and risky access paths that standard IAM tools miss.
Machine identities (service accounts, Lambda functions, containers) often hold excessive admin rights. ZERO-X tracks non-human activities, maps their actual usage against configured access policies and enables automated rightsizing to secure machine-to-machine interactions.
No. ZERO-X analyzes activity logs over time to ensure that only unused privileges are flagged. You can review auto-generated, optimized policies before applying them or utilize Just-In-Time (JIT) access to give developers on-demand elevated rights without persistent exposure.
Yes. ZERO-X standardizes identity entitlement visibility across AWS, Microsoft Azure, Google Cloud Platform (GCP) and Kubernetes under a single unified dashboard.
Most major security frameworks mandate the Principle of Least Privilege (PoLP). ZERO-X automates continuous evidence gathering, demonstrates tight privilege controls and provides audit-ready reports on identity governance.
Ready to Eliminate Cloud Identity Risks?
Get full visibility into your cloud entitlements and enforce least privilege in less than 15 minutes.
Ready to Eliminate Cloud Identity Risks?
Get full visibility into your cloud entitlements and enforce least privilege in less than 15 minutes.

