Secure Container Workloads from Registry to Production. End-to-End K8s Posture & Vulnerability Management.
Gain complete visibility across your Kubernetes clusters, container images, and runtime workloads. Detect misconfigurations, eliminate image vulnerabilities and automate remediation before risks reach production.

Secure Container Workloads from Registry to Production. End-to-End K8s Posture & Vulnerability Management.
Gain complete visibility across your Kubernetes clusters, container images, and runtime workloads. Detect misconfigurations, eliminate image vulnerabilities and automate remediation before risks reach production.
Core Value Proposition
Traditional K8s Security vs. Zero-X Cloud
The K8s Security Bottleneck
Vulnerable Container Images: Outdated base images and third-party packages deployed into live clusters.
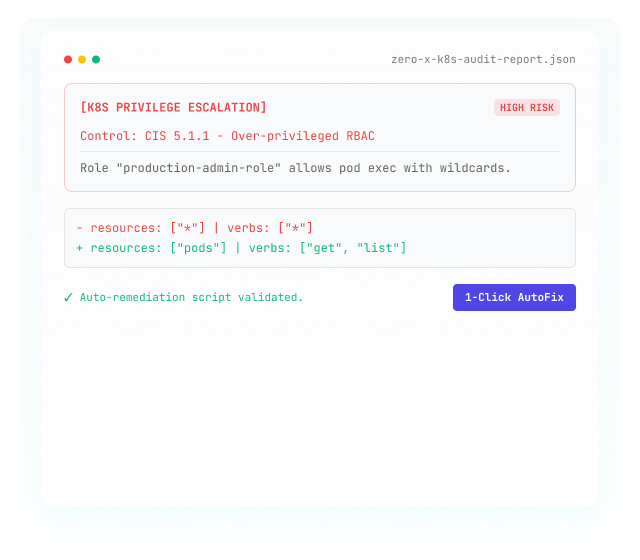
Complex K8s Misconfigurations: Over-privileged RBAC, exposed secrets and unencrypted pod communications.
Alert Fatigue & Slow Patching: Hundreds of raw CVEs without clear attack context or fixes.

The Zero-X Solution
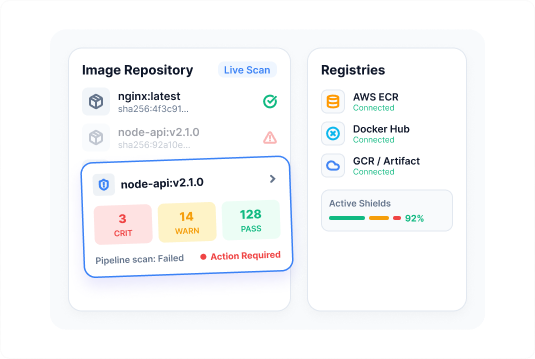
End-to-End Image Scanning: Automated scanning across build, container registries (ECR, GCR, ACR) and runtime.
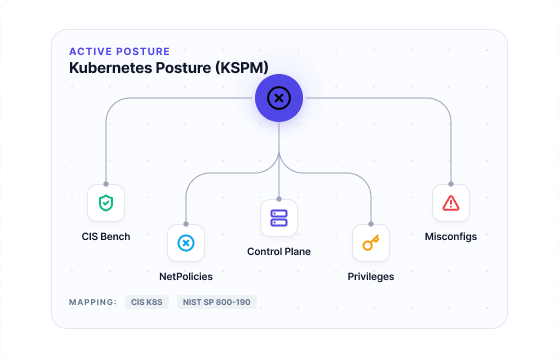
Automated KSPM: Kubernetes Security Posture Management continuously enforces K8s hardening standards
AI 1-Click AutoFix: Contextual threat prioritization with automated PRs and IaC fixes.
Core Value Proposition
Traditional K8s Security vs. Zero-X Cloud
The Zero-X Solution
key Capabilities
Core Platform Capabilities

Container Image Vulnerability Scanning
Continuously scan container images for known vulnerabilities (CVEs), embedded secrets, open-source dependency bugs and malware across your registries (ECR, GCR, ACR, Docker Hub) and CI/CD pipelines.

Kubernetes Security Posture Management
Identify dangerous cluster-level misconfigurations, root privileges, exposed control planes and weak NetworkPolicies. Map your Kubernetes environment against CIS Kubernetes Benchmarks and NIST standards.

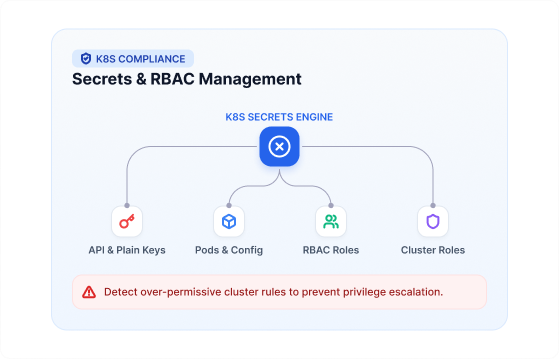
K8s Secrets & Access Control (RBAC) Management
Detect exposed hardcoded secrets, plain-text API keys and over-permissive Role-Based Access Controls (RBAC) across pods, configmaps and cluster roles to prevent privilege escalation.

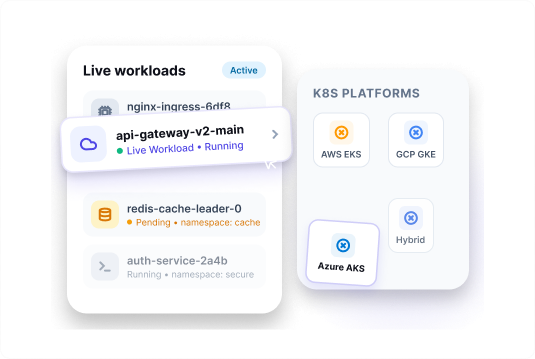
Runtime Workload & Cluster Visibility
Agentless and lightweight cluster monitoring tracks live workloads, running pods and worker nodes across managed cloud environments (AWS EKS, Google GKE, Azure AKS) and self-hosted Kubernetes clusters.
key Capabilities
Core Platform Capabilities

Container Image Vulnerability Scanning
Continuously scan container images for known vulnerabilities (CVEs), embedded secrets, open-source dependency bugs and malware across your registries (ECR, GCR, ACR, Docker Hub) and CI/CD pipelines.

Kubernetes Security Posture Management
Identify dangerous cluster-level misconfigurations, root privileges, exposed control planes and weak NetworkPolicies. Map your Kubernetes environment against CIS Kubernetes Benchmarks and NIST standards.

K8s Secrets & Access Control (RBAC) Management
Detect exposed hardcoded secrets, plain-text API keys and over-permissive Role-Based Access Controls (RBAC) across pods, configmaps and cluster roles to prevent privilege escalation.

Runtime Workload & Cluster Visibility
Agentless and lightweight cluster monitoring tracks live workloads, running pods and worker nodes across managed cloud environments (AWS EKS, Google GKE, Azure AKS) and self-hosted Kubernetes clusters.
How It Works
4-Step K8s Protection Workflow
STEP 01 • CONNECTION
Connect Your Cluster
Connect your EKS, GKE, AKS or native Kubernetes clusters effortlessly with lightweight, secure integration
STEP 02 • DISCOVERY
Deep Container & Manifest Discovery
Zero-X scans container images, YAML manifests, Helm charts and cluster configurations for security gaps.
STEP 03 • PRIORITIZATION
Risk Mapping & Prioritization
Correlate container vulnerabilities with actual cluster reachability to prioritize critical threats over background noise.
STEP 04 • REMEDIATION
AI Remediation & Enforcement
Generate Git branch PRs and code updates automatically—allowing developers to resolve risks directly within their workflow.
Intergrations
Works With Your Existing Stack
Effortlessly connect your projects from different cloud and code platforms.
FREQUENTLY ASKED QUESTIONS
Common Questions
Zero-X supports managed cloud services including AWS EKS, Google GKE and Azure AKS, as well as self-hosted Kubernetes clusters. It integrates directly with major container registries like Amazon ECR, Google Artifact Registry (GAR/GCR), Azure Container Registry (ACR), and Docker Hub.
Both. Zero-X shifts security left by scanning images in your CI/CD pipelines and registries before deployment, while continuously scanning active containers running in production for new zero-day vulnerabilities.
Zero-X evaluates your cluster's RBAC settings, network policies, pod security standards and host configurations against CIS Benchmarks and built-in security policies to flag excessive permissions, root access, or unencrypted traffic.
Instead of manually rewriting deployment manifests or editing Helm charts, Zero-X automatically generates corrected YAML code or Pull Requests (PRs) to patch vulnerable base images and fix misconfigurations instantly.
Lock Down Your Kubernetes Clusters and
Container Workloads Today.
Gain complete visibility into your cloud-native stack and automate K8s security with Zero-X.
Lock Down Your Kubernetes Clusters and Container Workloads Today.
Gain complete visibility into your cloud-native stack and automate K8s security with Zero-X.